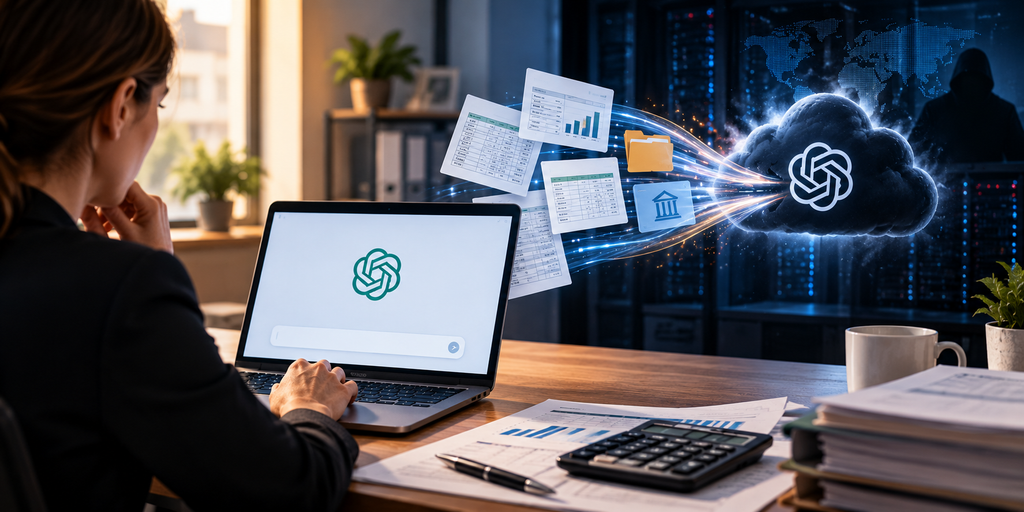
The security risk with AI bookkeeping tools is rarely the tool itself. It is what a staff member quietly does with one: open an unapproved assistant, paste in a client’s bank data or a payroll file to save ten minutes, and move on. That pattern has a name now, shadow AI, and it has become the dominant way client data slips out of a firm’s control.
The numbers behind it are not small. IBM’s 2026 Cost of a Data Breach Report found that shadow AI- employees using AI tools their firm never approved- now factors into 43% of AI-related security incidents, more than double the year before. One in four malicious breaches that year were AI-enabled. And Varonis reported that 99% of organizations have sensitive information reachable through generative AI copilots or unauthorized AI apps. For a bookkeeping or accounting firm, “sensitive information” is your clients’ financial records, which makes this less of an abstract IT concern and more of a direct professional risk.
What’s actually at stake for a firm
When a staff member enters client data into an outside AI tool, that data leaves your environment and becomes something a third party now holds, stores, and potentially uses to train a model. You often cannot say where it went or get it back. For a firm, three things ride on that. The first is client trust, which rarely survives a breach intact, and a lost client is far more expensive than the time any AI tool saved. The second is your regulatory position: under the FTC Safeguards Rule and IRS data-security expectations, a vendor processing client financial data is a service provider you are supposed to vet and document, and an AI tool nobody approved is a vendor nobody vetted. The third is cost. IBM put the average AI-enabled breach at around $6 million, and while most small firms are nowhere near that scale, the direction is clear enough that cyber-insurers have started asking about AI use on renewal forms.
Why firms are exposed
Most firms are exposed for a simple reason: adoption ran ahead of any rules. People started using AI tools because they helped, before anyone wrote down which tools were allowed or what could go into them. IBM found that about two-thirds of breached organizations lacked a complete AI governance policy, which is another way of saying the staff were using AI faster than the firm was governing it. The problem compounds when tools share logins. One report put AI-agent security incidents at 54% of enterprises, and in a firm that runs several AI tools on a shared credential, a single compromised login can expose every client at once. None of this requires a sophisticated attacker. It just requires a gap between what people do and what the firm has decided they should do.
How to reduce the risk
The fix is mostly organizational, and none of it is expensive. These are the steps that close the gap.
We go deeper on a couple of these elsewhere: our look at running AI bookkeeping tools inside hosted QuickBooks covers how the compatible tools fit, and our guide to the WISP requirements covers the documentation side.
Where hosting fits, and where it doesn’t
Hosting sits on one part of this, not the whole of it. When your accounting software and client data run in a hosted environment, that data lives in one access-controlled, backed-up place rather than copied across laptops and inboxes, which shrinks the surface shadow AI can pull from and gives you a documentable service provider for your WISP. What hosting does not do is write your AI policy, approve your tools, or stop someone from opening an unapproved assistant in a browser tab. The organizational steps above are the actual fix. Hosting is the foundation they sit on, a safer place for the data to live, not a substitute for deciding how it gets used.
This article is general information, not legal or compliance advice. Confirm your obligations against current FTC and IRS guidance and a qualified advisor.
AI and client-data security questions
What’s the main security risk with AI bookkeeping tools?
Shadow AI: staff using unapproved tools and entering client financial data into them. The tool itself may be fine. The exposure is client data going somewhere nobody vetted, documented, or controls, which is exactly what makes it hard to detect or undo.
Does using AI tools affect my FTC Safeguards or WISP obligations?
Yes. An AI vendor processing client financial data is a service provider you are expected to vet and document. Using AI does not remove that duty; it adds a vendor to your WISP. An unapproved tool is a vendor nobody assessed, which is the part regulators and insurers care about.
Does hosting make AI tools safe?
No. Hosting gives client data a controlled, access-controlled home instead of scattered laptops, which is a stronger foundation. It does not write your AI policy or stop someone using an unapproved tool. The policy and the approved-tool list are the fix; hosting supports them rather than replacing them.
Book a 15-minute call → to talk through keeping client data in one controlled place as you add AI tools to your workflow.
Leave a Reply