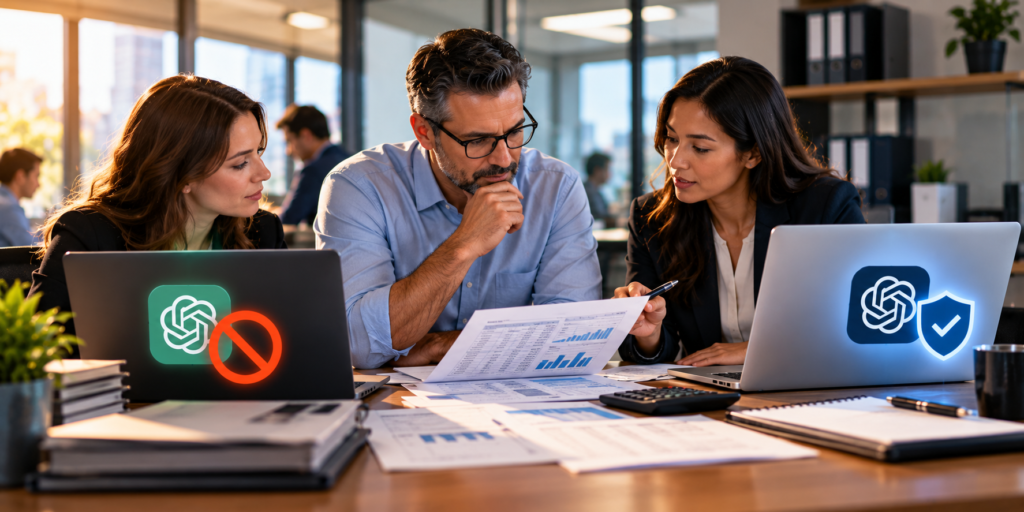
Should your staff use ChatGPT with client financials? The question comes up in every firm now, and the answer is more workable than either extreme suggests. Banning AI outright is unrealistic and hands an advantage to firms that use it well. Letting staff paste client data into whatever tool they like is a data-security problem waiting to surface. An AI policy for an accounting firm sits between those, and it is simpler than most owners fear: match the tool to the data, draw one hard line, and write it down.
The short answer
No client-identifiable financial information should go into a personal or consumer AI account, such as a free or personal ChatGPT login. For anything touching client data, use a business-tier AI tool that contractually keeps your data out of model training, and that you have vetted and documented like any other service provider. For general work that involves no client-identifiable data, staff can use AI freely. That is the whole policy in three sentences. The rest is detail.
Why consumer ChatGPT is the wrong place for client data
The difference between consumer and business AI tools is not marketing; it is in the data terms. On consumer tiers, OpenAI may use your conversations to improve its models by default unless you opt out, while on its business and enterprise tiers, OpenAI states it does not train on your business data by default. That alone tells you a personal ChatGPT account is the wrong home for a client’s bank records. The larger risk is more human than legal: staff reach for the personal account they already have, which quietly puts client data on the training-by-default tier without anyone deciding it should. And once text is submitted, you cannot pull it back. For a firm that answers to the FTC Safeguards Rule, an AI tool processing client data is a service provider you are expected to vet, and a consumer account is a vendor nobody assessed. Even on a business tier, the data policy is the floor, not the finish, because it does not stop a careless paste or remove your duty to review what the tool produces.
What a practical AI policy covers
A usable policy is short, often a page, and covers these points. It does not need legal language to work.
What staff can use AI for
A policy that is all restrictions gets ignored, so it helps to be clear about what is encouraged. Staff can lean on AI for plenty of real work without touching client data: drafting an email or a client letter from scratch, summarizing a public tax change, explaining a concept in plainer language, building a template or a checklist, or brainstorming how to approach a problem. The rule is about the data, not the task. If nothing client-identifiable goes into the tool, the work is fair game, and it is where most of the day-to-day time savings actually come from. Framing the policy around what staff can do, alongside the one thing they cannot, tends to get followed, where a blanket “no AI” does not.
Where hosting fits
Hosting is one supporting piece, not the answer. When your accounting software and client data run in a hosted environment, that data lives in one access-controlled, backed-up place rather than copied across personal devices, which gives your policy a smaller surface to defend and a documentable service provider for your WISP. What hosting does not do is write the policy, approve the tools, or stop someone opening a personal AI account in a browser tab. The written policy and the approved-tool list are the controls that actually govern AI use. Hosting makes them easier to hold, which is a real but modest role. We cover the risk side in our note on the security risk behind AI bookkeeping tools, and the documentation side in our guide to the WISP requirements.
This article is general information, not legal or compliance advice. Confirm your obligations against current FTC and IRS guidance and a qualified advisor, and review any tool’s current terms before you rely on them.
Firm AI policy questions
Can staff use ChatGPT at an accounting firm?
Yes, for general work like drafting and research, but not with client-identifiable financial data in a personal or consumer account. A good policy matches the tool to the data rather than banning AI, so staff get the time savings without putting client information somewhere you cannot control.
Why is consumer ChatGPT a problem for client data?
On consumer tiers, inputs may be used to train models by default, and staff often use personal accounts for work, so client data lands somewhere you do not control and cannot retract. Business tiers exclude your data from training, but even then the data policy is only the floor, not a substitute for care.
Does hosting solve the AI policy problem?
No. Hosting keeps client data in a controlled place and supports documenting your vendors, but it does not write your policy or stop someone pasting data into a browser. The written policy and the approved-tool list are the controls that actually govern AI use.
Do I really need a written AI policy?
If your staff use AI at all, yes. It is the same vendor-oversight and data-security expectation the FTC Safeguards Rule and IRS already place on your firm, applied to a new category of tool. A short written policy is far easier to defend than an unwritten assumption.
Book a 15-minute call → to talk through keeping client data in one controlled place as your firm sets its AI rules.
Leave a Reply